Governance, Risk, and Compliance Solutions
One of the biggest cyber security challenges that today’s businesses are facing is a lack of structure. Without a clear framework in place, it can be difficult to track what’s already been done, what still needs attention, and where the real gaps lie.
That lack of visibility can lead to inconsistencies, missed vulnerabilities, and uncertainty around accountability, leaving organisations open to unnecessary risk.
At London Risk Consulting Group, we help you take control of information security by building strong governance, risk management, and compliance foundations.
We’re here to give you the services, insight, and support needed to develop a strategic roadmap to success, make smarter decisions, and protect your business with confidence.
A Business Aligned Approach
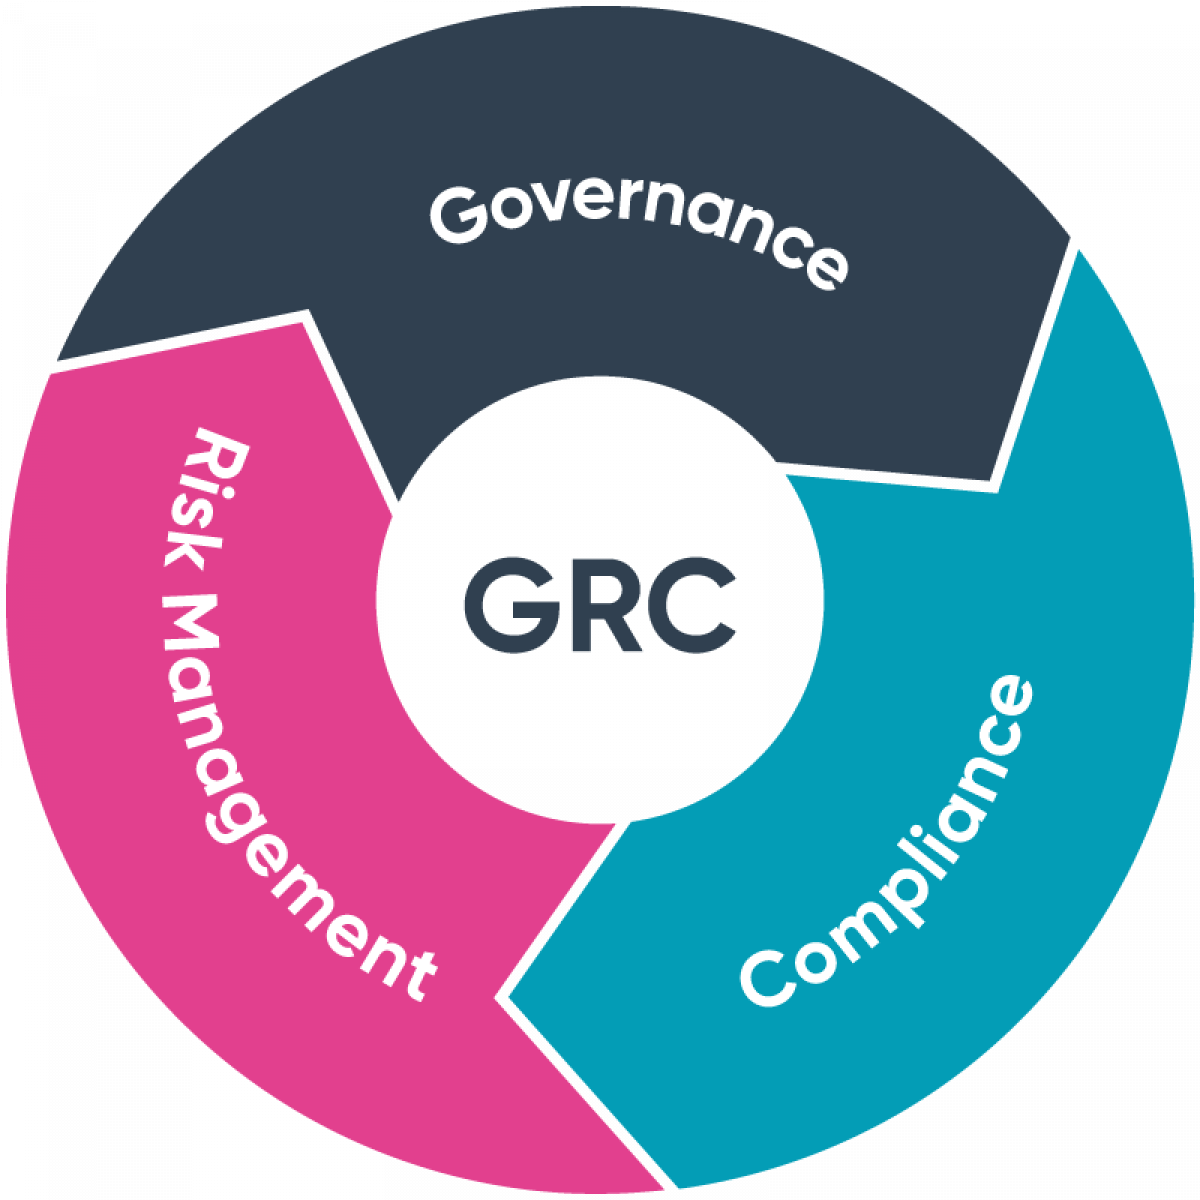
Our dedicated Governance, Risk, and Compliance service is designed to give you a systematic, business-aligned approach to managing cyber risk. We work closely with organisations across a wide range of sectors to build a risk management framework that’s proportionate, practical, and fully tailored to each company’s unique needs.
As part of our service, we’ll work with you to:
- Develop a custom risk management framework aligned with industry standards
- Create information security policies that support day-to-day operations
- Implement methods for identifying, evaluating, and prioritising information risks
- Fully assess the business impact of cyber threats and vulnerabilities
- Generate risk registers and form clear, structured assessments
- Embrace the most appropriate risk treatment plan
Everything we do is focused on helping you reduce risk, improve compliance, and build a strong, resilient security posture, without overcomplicating the process.
Removing the Guesswork
We understand that many businesses don’t know where to begin when it comes to governance and risk. That’s why we make it our priority to remove the guesswork.
Our consultants don’t just apply generic templates; instead, we take the time to fully understand your organisation, your individual risks, and the challenges you face.
With deep expertise in recognised frameworks such as ISO 27001, and hands-on experience across a wide range of sectors, we know how to turn regulatory expectations into meaningful business practices. We help you build structure where there is none, create clarity where there’s confusion, and make risk management an integrated part of how your business works… not just a compliance tick-box.
If you want practical support that strengthens your cyber security posture from the inside out, we’re here to help you put the right foundations in place. Get in touch to schedule a consultation.