Services
Governance, Risk, and Compliance Solutions
One of the biggest cyber security challenges that today’s businesses are facing is a lack of structure. Without a clear framework in place, it can be difficult to track what’s already been done, what still needs attention, and where the real gaps lie.
That lack of visibility can lead to inconsistencies, missed vulnerabilities, and uncertainty around accountability, leaving organisations open to unnecessary risk.
At London Risk Consulting Group, we help you take control of information security by building strong governance, risk management, and compliance foundations. We’re here to give you the services, insight, and support needed to develop a strategic roadmap to success, make smarter decisions, and protect your business with confidence.
A Business Aligned Approach
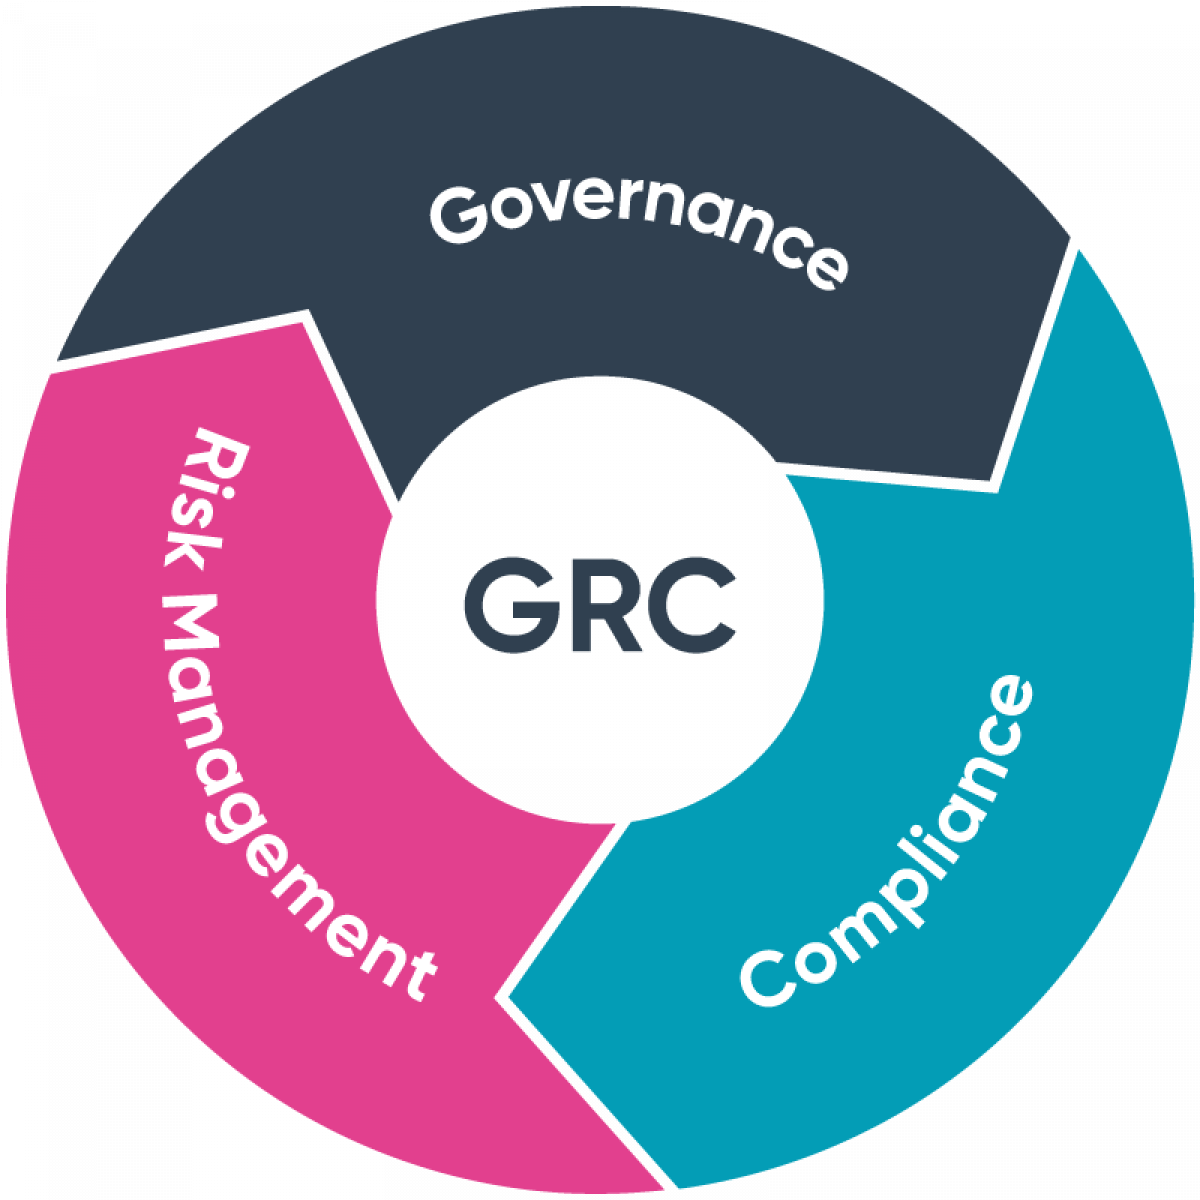
Our dedicated Governance, Risk, and Compliance service is designed to give you a systematic, business-aligned approach to managing cyber risk. We work closely with organisations across a wide range of sectors to build a risk management framework that’s proportionate, practical, and fully tailored to each company’s unique needs.
As part of our service, we’ll work with you to:
- Develop a custom risk management framework aligned with industry standards
- Create information security policies that support day-to-day operations
- Implement methods for identifying, evaluating, and prioritising information risks
- Fully assess the business impact of cyber threats and vulnerabilities
- Generate risk registers and form clear, structured assessments
- Embrace the most appropriate risk treatment plan
Everything we do is focused on helping you reduce risk, improve compliance, and build a strong, resilient security posture, without overcomplicating the process.
Removing the Guesswork
We understand that many businesses don’t know where to begin when it comes to governance and risk. That’s why we make it our priority to remove the guesswork.
Our consultants don’t just apply generic templates; instead, we take the time to fully understand your organisation, your individual risks, and the challenges you face.
With deep expertise in recognised frameworks such as ISO 27001, and hands-on experience across a wide range of sectors, we know how to turn regulatory expectations into meaningful business practices. We help you build structure where there is none, create clarity where there’s confusion, and make risk management an integrated part of how your business works… not just a compliance tick-box.
If you want practical support that strengthens your cyber security posture from the inside out, we’re here to help you put the right foundations in place. Get in touch to schedule a consultation.
Cyber Security, Control Testing, and Review
Even the most cleverly designed and well-documented security framework can fall short if the controls aren’t properly implemented, monitored, maintained, and updated as the landscape evolves. Without regular testing and independent review, it’s difficult to know whether your security measures are continuing to do what they’re supposed to, or if gaps in design or execution are leaving you at risk. At London Risk Consulting, we provide in-depth cyber security control testing and review services to verify the effectiveness of your security measures.
Whether you’re reviewing your own internal processes or assessing the security of third-party providers, we give you the clarity you need to take confident, informed action.
Independent Testing and Review
Our independent testing and review service gives you a clear, transparent view of how well your current controls are working, and where improvements are needed.
We work with organisations to assess their internal security practices, ensure alignment with industry standards, and identify weaknesses across the environment. We can also evaluate the security posture of any third-party providers you’re working with, helping you to effectively manage risks across your supply chain.
As part of our service, we’ll work with you to:
- Assess compliance with international security standards (e.g. ISO 27001, NIST)
- Review existing security policies and technical controls
- Evaluate the design effectiveness and operational effectiveness of your control environment
- Identify areas where controls are missing, outdated, and/or poorly designed and implemented
- Conduct internal reviews of your cyber security / risk management framework
- Review and assess third-party service providers to expose potential weak points
Our assurance methodology is comprehensive, structured, and tailored to your needs, ensuring you get the insight needed to take action, without complexity.
Why Choose Us for Your Cyber Security Needs?
We know that cyber security controls often look strong on paper. However, only independent testing and review can fully reveal whether they truly effective and hold up under pressure. That’s why our focus is on real-world results and outcomes, not just box-ticking for the sake of it.
Our team has extensive experience in both industry frameworks and practical security implementation. We take the time to understand how your organisation works, so we can offer relevant insights, not generic findings. We also recognise the growing importance of third-party risk and bring a clear, methodical approach to supplier reviews that can be instrumental in strengthening your security posture.
Whether you’re preparing for a certification audit, addressing regulatory requirements, or simply looking to raise internal standards, we’ll help you uncover hidden risks and build a clearer picture of your organisation’s resilience.
If you want assurance that your security controls are fit for purpose or are looking for expert guidance on where you need to improve, our team is ready to help.
Cyber Security Maturity Assessment
Cyber security isn’t just about having the right tools or ticking off compliance requirements. It’s about understanding how well your organisation is positioned to respond to evolving threats; it’s about having a well-rounded approach.
Many businesses are questioning how developed their security programme really is. Are policies consistent across teams? Are staff fully aware of their responsibilities? Do controls actually align with the risk profile and business priorities? Without a clear view of your overall cyber maturity, it can be difficult to make informed decisions, prioritise improvements, or demonstrate progress to the board and to investors.
At London Risk Consulting, we provide a strategic, business-aligned assessment that looks beyond individual controls. Our Cyber Security Maturity Assessment helps you to both see and understand the bigger picture… and how to strengthen it.
A Comprehensive Evaluation
Our Cyber Security Maturity Assessment (CMA) offers a comprehensive evaluation of your organisation’s security capabilities across three key dimensions: people, process, and technology. We look at how well your security practices are embedded into day-to-day operations, how consistent and scalable your governance is, and how prepared your teams are to respond to incidents.
As part of our service, we’ll work with you to:
- Review your current level of cyber maturity against established frameworks
- Assess strengths and weaknesses across people, process, and technology
- Identify inconsistencies or gaps that may limit long-term resilience
- Map findings to risk appetite, business goals, and regulatory expectations
- Prioritise recommendations based on risk exposure and impact
- Create a clear, practical roadmap for building maturity over time
Our approach gives you an end-to-end view of where your organisation stands, and what needs to change to boost performance, reduce risk, and show progress.
Understanding Your Operational Realities
Our maturity assessments focus on the real-world application of cyber strategy. We don’t just audit policies or test controls; we look at how security is embedded into your organisation, from leadership decisions right down to daily behaviours.
Our team combines experience in cyber governance, risk, compliance, and security operations, allowing us to assess both the high-level view and the operational realities. We tailor every action to your specific business context, helping you build a maturity roadmap that’s practical, achievable, and aligned with your business.
If you need clarity on where you stand and want to know how to move forward with confidence, we’re here to help you shape a more resilient and secure future.
ISO 27001 Consultancy
For many organisations, improving cyber security isn’t just about protection; it’s about being able to prove that security is a priority. And that’s where ISO 27001 comes in. Whether you’re aiming to meet regulatory requirements, contractual obligations, win new business, or strengthen internal governance, ISO 27001 is a globally recognised standard for managing information security in a consistent, structured, and demonstrable way. Unfortunately, implementation can feel complex without the right guidance.
From documentation to risk assessments, the process involves a level of planning and structure that many businesses haven’t yet built. Without support, it can be easy to get stuck, delay progress, or miss key requirements that put certification at risk. At London Risk Consulting, we provide ISO 27001 consultancy to help you meet the standard confidently, building a security framework that supports your goals.
Supporting You in Your Journey
We support organisations at every stage of their ISO 27001 journey, from initial gap analysis and implementation through to successful accredited certification. Whether you’re starting from scratch or improving an existing information security management system (ISMS) we’ll tailor our approach to suit your own business timescales, resources, and in-house expertise.
As part of our service, we’ll work with you to:
- Assess your current readiness and identify key gaps
Design an ISO 27001-compliant Information Security Management System (ISMS) - Establish the required policies, controls, and governance structures
- Carry out risk assessments and internal audits as necessary
- Prepare your internal teams for audit and certification
- Maintain and improve your ISMS over time
We take a flexible, business-focused approach, so whether you need light-touch guidance, full implementation support, or a fast-tracked project aligned to a specific contract or deadline, we can tailor our solution to your precise needs.
Why Choose Us?
We understand that every organisation is different, and so are the reasons for pursuing ISO 27001 certification. That’s why our consultancy service is never off-the-shelf. We focus on your business requirements, helping you embed cyber security in a way that makes sense for your people, your systems, and your clients.
Our consultants bring real-world experience and deep knowledge of the ISO 27001 standard, giving you practical advice that cuts through complexity. We work as an extension of your team, translating requirements into actions and helping you to build a strong system that’s robust, scalable, and certification ready.
Whether you need end-to-end support or targeted guidance, our expert team is here to make ISO 27001 work for your business… not the other way around.
Data Loss Prevention
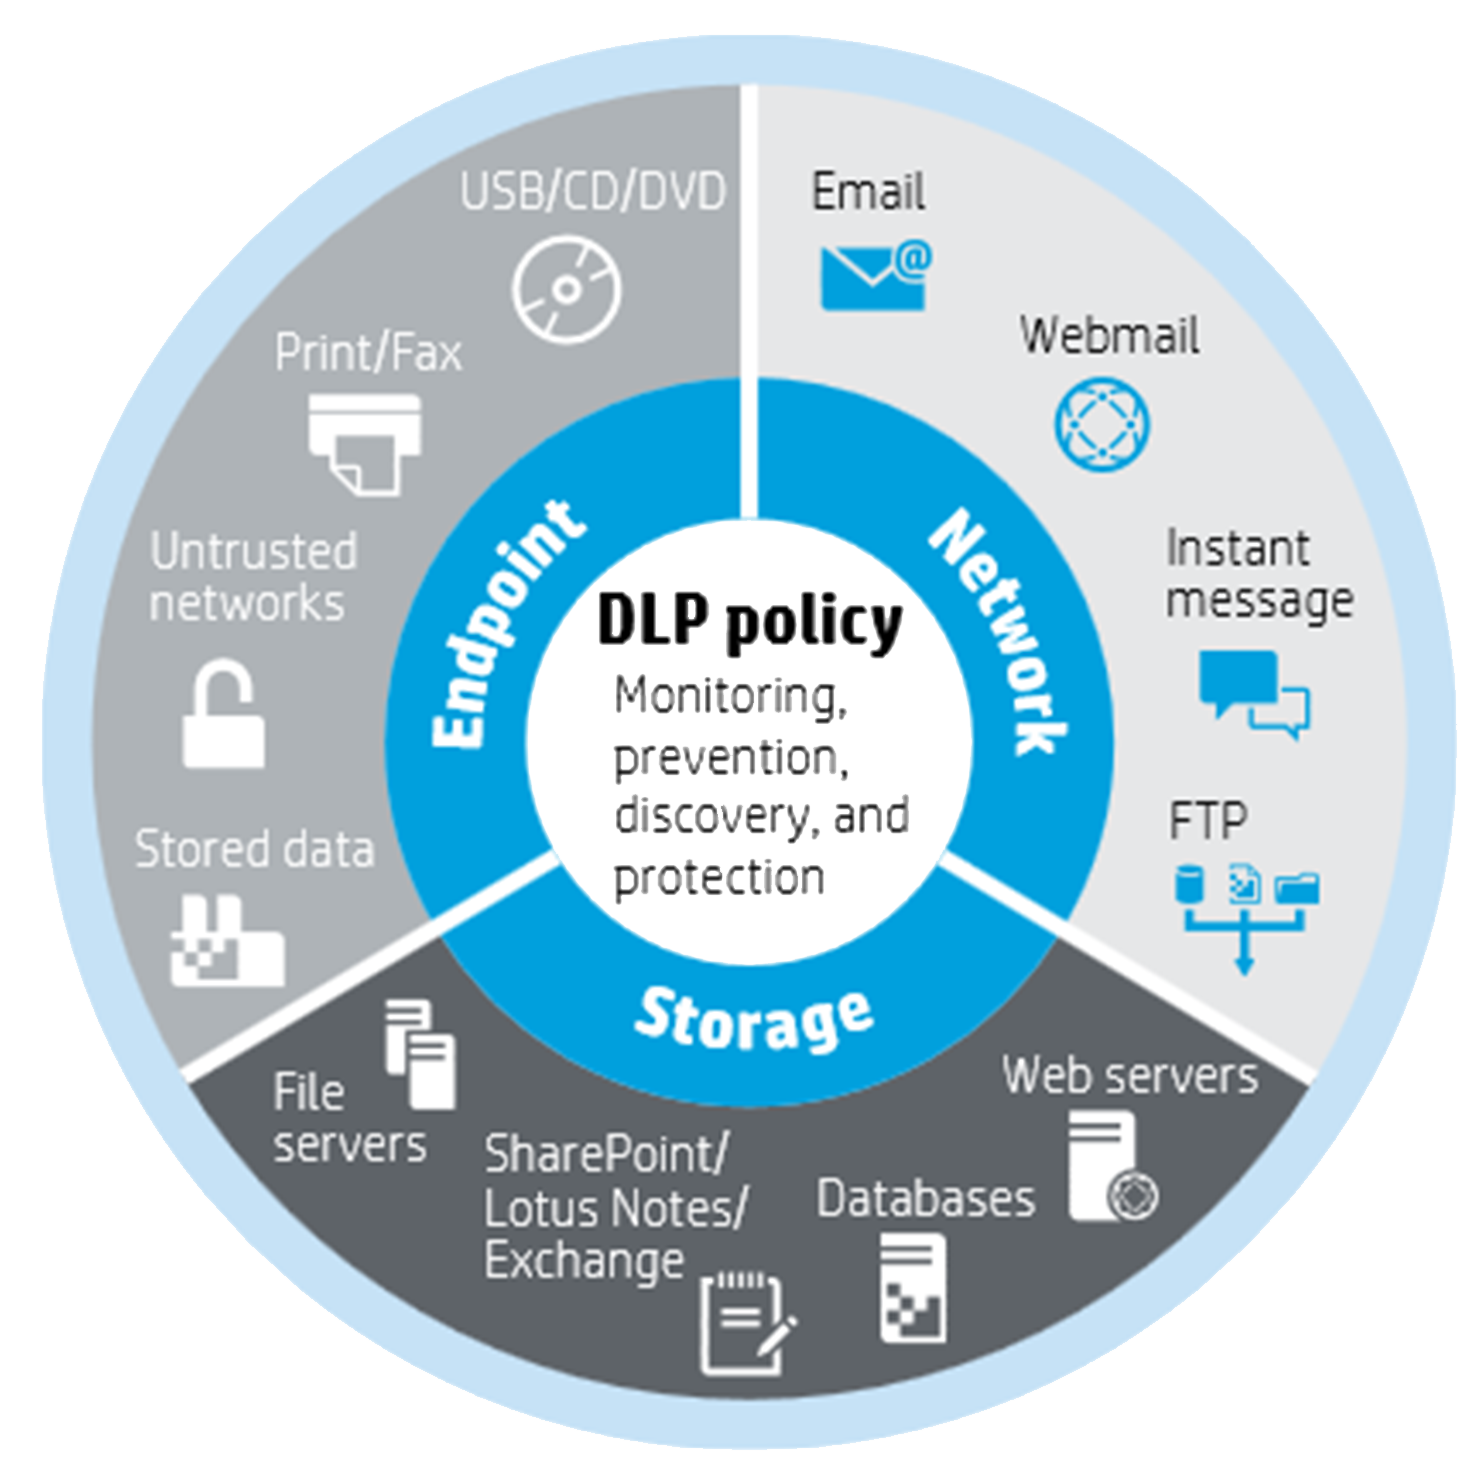
Most businesses today hold vast amounts of sensitive information, ranging from financial data and customer records to internal strategies and intellectual property. But in many cases, organisations don’t always have full visibility of how that data moves, who has access to it, or how easily it could be taken or accidentally lost. While targeted cybercrime is a huge challenge right now, the risk isn’t always external. Insider threats – whether unintentional or deliberate – are a growing concern for businesses of all sizes. Without the right controls and monitoring in place, it’s possible for staff or third parties to exfiltrate critical information without detection.
At London Risk Consulting, we help you take a proactive approach to protecting your data. Our Data Loss Prevention (DLP) service provides insight into how business data may be exposed to theft, giving you a practical plan for reducing that risk.
Recommendations Tailored to Your Priorities
Our DLP service involves a thorough internal assessment of how your data could be accessed, misused, or exfiltrated, with a particular focus on insider risk. We look at both intentional and unintentional data loss scenarios, and provide clear, prioritised recommendations to reduce your exposure and maximise your digital security.
As part of our service, we’ll work with you to:
- Assess your current exposure to data loss and exfiltration risks
- Simulate insider threat scenarios from the perspective of an internal user
- Identify weaknesses in access controls that would enable users to access, extract, and exfiltrate data without authorisation, monitoring, detective and preventative controls
- Evaluate the likelihood and impact of data theft across different business areas
- Review existing detection and response processes
- Implement mitigation recommendations aligned with business risk
We also assess the broader impact of data loss – including financial, reputational, regulatory, and operational consequences – to help you prioritise remediations .
A Deep Understanding of Security Risk
Protecting your data doesn’t just require the right tools; it requires insight into how your organisation really operates. That’s why our DLP assessments go beyond surface-level checks. We take a real-world approach that reflects how insider threats can unfold in practice and explores what can be done to stop them.
Our expert team brings a deep understanding of security risk, insider threat modelling, and data protection strategies. We help you turn abstract risks into clear action points, grounded in your business context. Whether you’re concerned about compliance, operational resilience, or reputational damage, we help you build defences that actually work out there in the real world… not just on paper.
If you want clarity on how secure your data really is, we’re here to help.